Secure API Key Management for Frontend Developers
Frontend developers often struggle with securely calling APIs that require authentication. Storing API keys directly in frontend code risks exposing secrets to anyone inspecting the app, yet many developers still do it out of convenience or lack of better options. What’s missing is a lightweight platform that lets “vibe coders” — indie hackers, prototypers, and frontend-focused devs — store their API keys safely and call external services securely without spinning up backend infrastructure. A kind of “key vault as a service” designed specifically for client-side apps. It could proxy requests, inject credentials server-side, and return safe responses to the frontend — no backend setup required. This would empower solo builders to experiment, launch faster, and stay secure. For the thousands of devs shipping daily on Replit, Vercel, and Codesandbox, it could be the missing piece.
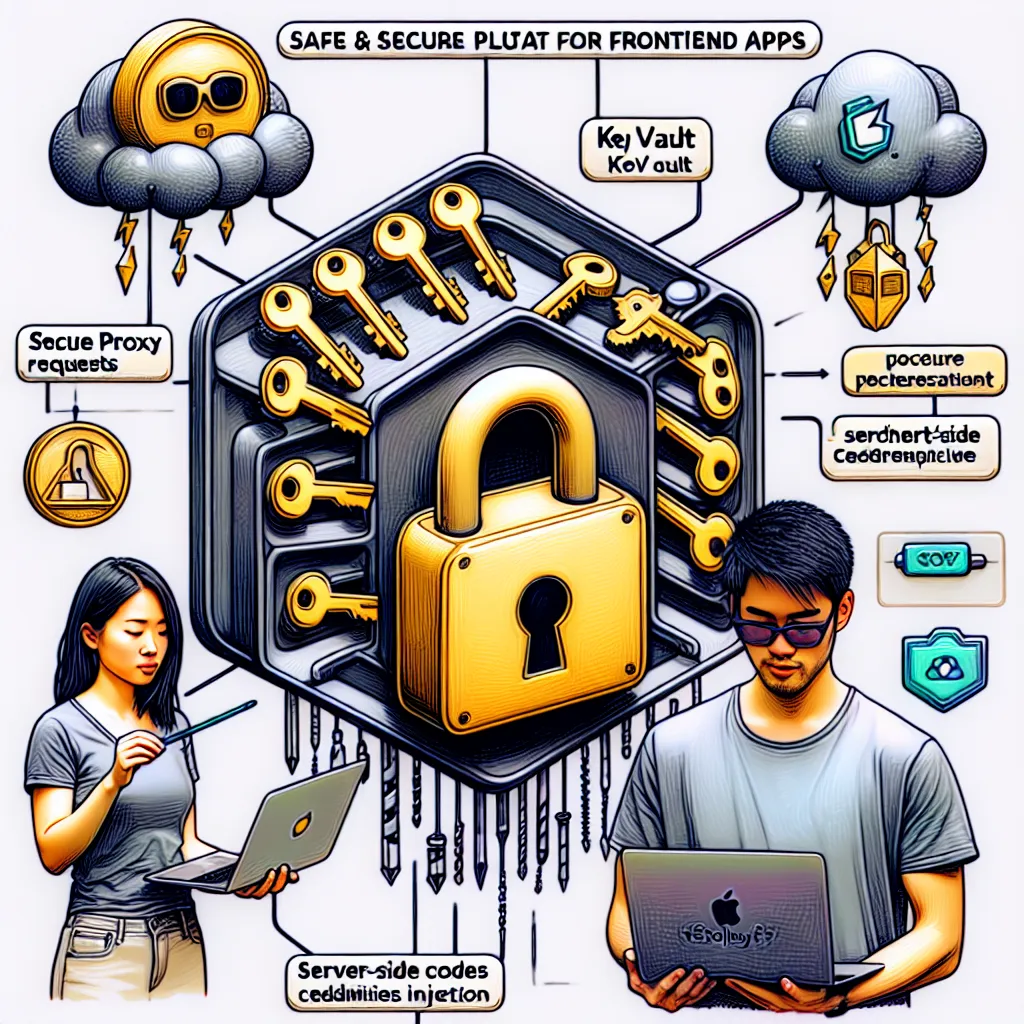
Description
No additional description provided.
The Pitch
Frontend developers often encounter challenges when it comes to securely calling APIs that require authentication. The direct storage of API keys within frontend code poses the risk of exposing these sensitive secrets to anyone who might inspect the application. Despite this risk, many developers continue to do so due to convenience or simply not knowing of a better alternative. There is a significant gap in the market for a lightweight platform specifically tailored for vibe coders — indie hackers, prototypers, and frontend-focused developers. These individuals need a way to securely store their API keys and invoke external services without having to manage backend infrastructure.
This scenario highlights the need for a key vault as a service, a platform expressly designed for client-side applications. Such a solution could proxy requests, inject credentials server-side, and return responses safely to the frontend without requiring any backend setup. It would enable solo developers to experiment more freely, launch their projects faster, and maintain security.
For developers frequently working with platforms like Replit, Vercel, and Codesandbox, where rapid prototyping and deployment are commonplace, this platform could fill a critical gap in their workflow. It would empower them to enhance their security practices effortlessly while staying focused on innovation.
The proposed platform would operate by allowing developers to store their API keys in a secure environment. The keys would never touch the client-side code. Instead, the platform would manage these keys and proxy requests to third-party services on behalf of the application. This proxying functionality ensures that sensitive credentials are used properly without being exposed.
Key features of the platform might include:
1. **Secure Storage**: API keys and credentials would be stored securely on the server, away from client-side exposure.
2. **Request Proxying**: The platform would handle requests to external services, injecting necessary credentials and forwarding the results to the client application.
3. **Easy Integration**: With SDKs or plugins designed to work seamlessly with popular development environments like Replit, Vercel, and Codesandbox, integration would be straightforward.
4. **Usage Monitoring**: Provide developers with insights into how their keys are being used, helping them track performance and detect potential abuse.
To facilitate the launch of this platform as a Minimum Viable Product (MVP), a combination of existing tools and infrastructure could be employed. Using serverless functions would be a cost-effective way to handle proxying without the need for a dedicated server setup. Additionally, integrating security-focused libraries can ensure that credentials are stored and managed securely.
The Go-To-Market (GTM) strategy would focus on engaging with communities of indie developers and frontend-focused forums to build awareness and trust. Offering a free tier with limited API requests could encourage adoption, with a paid tier available for those requiring higher usage limits or additional features.
As a business model, a subscription-based model is likely most effective, offering tiers based on request volume and additional features. Another approach could be usage-based billing to accommodate different scales of project requirements amongst target users.
By addressing this critical gap, the platform would provide immense value to developers who prioritize security and speed in their development process. Empowering developers to innovate without sacrificing security, this service represents a vital tool in the modern developer's toolkit.