Mapping Invisible Dependencies in AI Systems
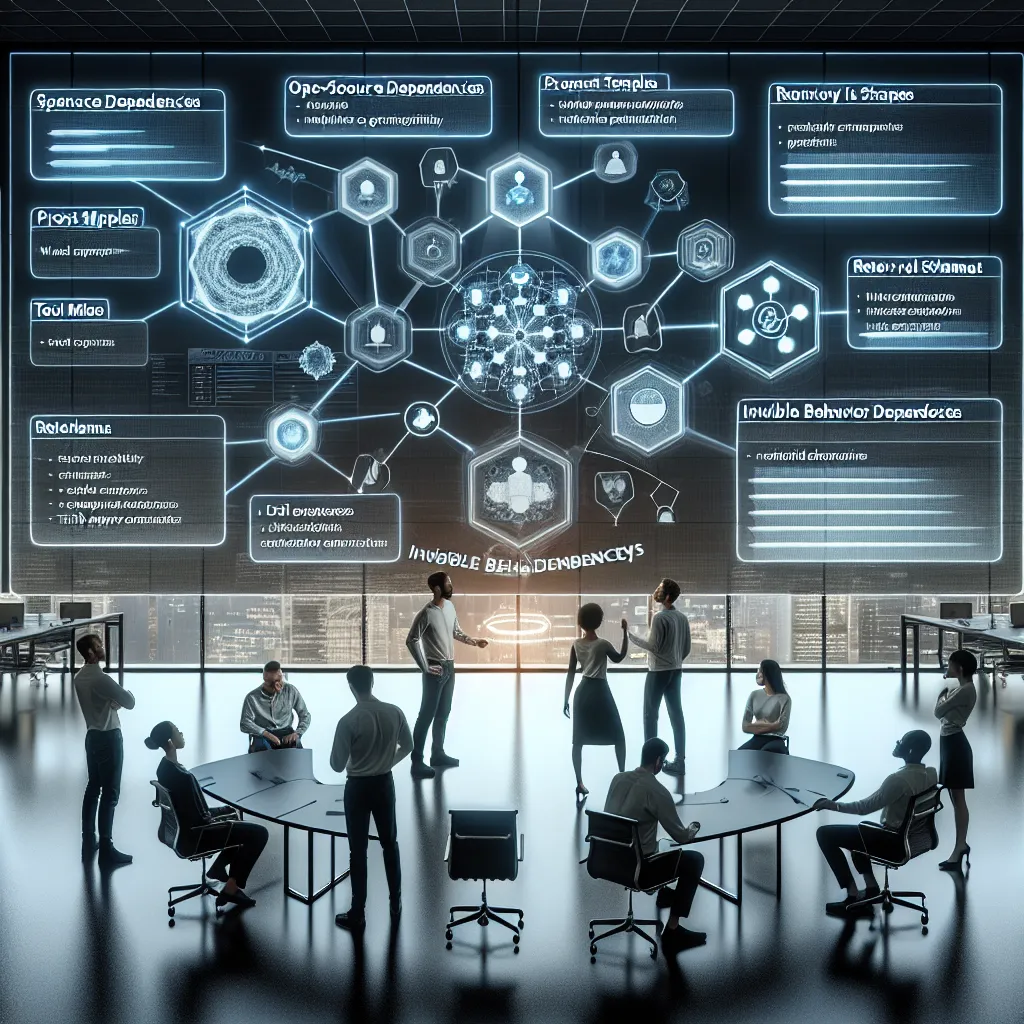
Modern security teams can tell you every open-source dependency in production—but ask them what prompts, tools, or MCP connectors their AI relies on, and the answer is usually “we think we know.” LLM systems introduce a new supply chain that isn’t code in the traditional sense: prompt templates, retrieval sources, tool schemas, and third-party connectors that silently shape behavior. A single unreviewed change can alter what the model sees, what it’s allowed to do, or where data flows—and none of this shows up in existing scanners. What should exist is a live dependency graph for AI behavior itself, mapping how prompts, tools, and MCP connections interact and flagging risk the same way we do for vulnerable libraries. As AI stacks become composable by default, the next generation of breaches won’t come from bad code—they’ll come from invisible behavior dependencies no one thought to audit.
Description
No additional description provided.
The Pitch
In today's digital landscape, the focus of security has traditionally been on identifying vulnerabilities within code, especially open-source dependencies in production. However, as AI systems and Large Language Models (LLMs) become integral to business operations, a new dimension of security has emerged. These systems rely not just on traditional code but on collections of prompts, tools, metadata connectors, and various external sources that collectively influence AI behavior. This introduces a novel type of supply chain, one that current security tools are not equipped to analyze or monitor effectively.
### The Problem
Current security frameworks fall short in fully understanding and auditing AI behavior. Security teams often have comprehensive insights into their software's open-source dependencies, yet they struggle to identify and assess the components that drive AI functionality. The challenge lies in the dynamic nature of AI systems, where a single unreviewed change—be it in prompt templates, data retrieval sources, tool schemas, or third-party connectors—can significantly alter outcomes, permissions, or data paths. These changes do not leave a trace in traditional code scans, creating a blind spot for potential vulnerabilities.
### The Solution
What is needed is a dynamic and interactive platform that functions as a live dependency graph for AI behavior. This platform would map out how various elements like prompts, tools, and connectors interact within an AI system. By visualizing these dependencies, it can identify and flag potential risks, just as security tools currently do with vulnerable software libraries. This solution would provide a new layer of transparency and control over AI systems, enabling security teams to preemptively address vulnerabilities in a proactive manner.
### Product Details
The proposed platform would include:
- **Dependency Mapping**: A feature that charts the interactions between all components influencing AI behavior, similar to a software dependency graph. - **Risk Assessment and Alerts**: Automated risk scoring for each component and interaction, with real-time alerts for any anomaly or unreviewed change. - **Audit Trail**: A comprehensive history of changes and interactions for accountability and forensic analysis. - **Integration with Existing Tools**: Seamless integration with current DevSecOps tools to ensure a cohesive security posture.
### Tools for MVP Launch
To quickly bring this solution to market as a Minimum Viable Product (MVP), these tools and strategies can be employed:
- **Platform Development**: Leverage cloud-based microservices architecture (e.g., AWS, Azure) to build the initial product rapidly. - **Dependency Graphing Tools**: Utilize graph database technologies like Neo4j for creating and managing the live dependency graphs. - **Real-time Monitoring**: Implement real-time analytics tools like Apache Kafka for monitoring interactions and flagging anomalies. - **User Interface Design**: Use frontend frameworks like React or Vue.js for an intuitive dashboard.
### Go-To-Market Strategy
- **Target Audience**: Focus on enterprises that heavily rely on AI and LLM systems, particularly in tech, finance, and healthcare sectors. - **Initial Rollout**: Begin with a beta program for select industry leaders to gain feedback and refine the product. - **Partnerships**: Collaborate with cybersecurity firms and AI model developers to extend reach and add credibility. - **Educational Campaigns**: Host webinars and create content around AI security to raise awareness about the unique challenges and the need for this solution. - **Sales Strategy**: Employ a direct sales approach for large enterprises while considering a self-service model for smaller companies.
### Business Model
The proposed platform could adopt a subscription-based model, offering tiered pricing based on the scale of operations and features required:
- **Basic Tier**: For smaller companies with fundamental dependency mapping and risk assessment capabilities. - **Professional Tier**: For medium-sized enterprises needing advanced features like integration with existing tools and detailed audit trails. - **Enterprise Tier**: Custom solutions for large organizations with comprehensive support, advanced analytics, and customizable dashboards.
The emphasis on capturing the nuances of AI's behavioral dependencies and potential vulnerabilities presents a unique opportunity to make AI adoption safer and more controllable. By offering security teams the tools to visualize, monitor, and manage these elements, this solution not only fills a critical gap but also sets a new standard for AI security.
---